Healthcare

Managed IT Services for Healthcare: HIPAA-Ready Service Management on One Platform

PHI raises the stakes on every record. An auditor wants to know who accessed what, who approved each change, and how fast the desk responded. Email doesn't survive that review. This page covers healthcare IT service management, not clinical staffing programs. Vivantio gives every request an owner, an SLA, and an audit trail, whether IT is run in-house, outsourced, or both.

Demo built around your organization's own request types. ~30 minutes.

100%
Audit trail coverage
3 wks
Typical time to go live
4.7★
Average G2 rating
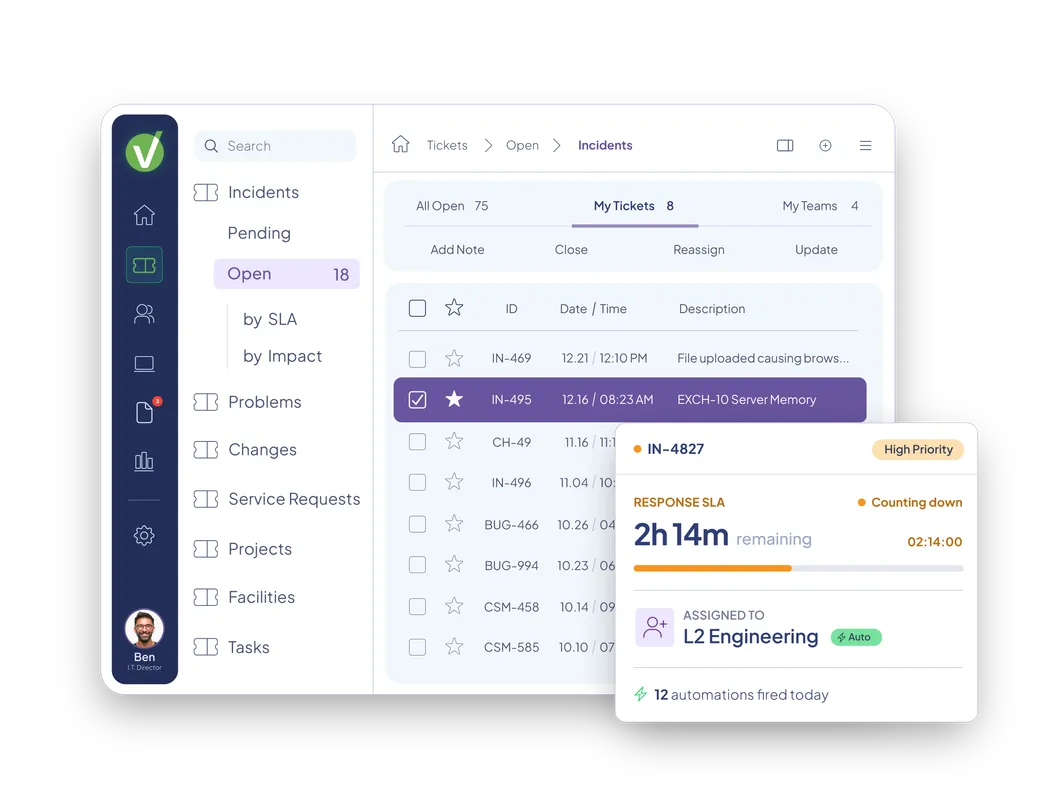
Incident and SLA tracking in Vivantio
One platform, either side of the desk

The platform underneath whichever model you run.

Vivantio is the service management platform healthcare organizations and their IT providers run on, not a managed services provider and not a clinical staffing platform. It sits underneath whichever model you choose, in-house, outsourced, or both, and gives every request an owner, an SLA, and an audit trail that holds up under HIPAA review.

Healthcare organizations and their IT providers run on Vivantio

What's actually included

What do managed IT services for healthcare include?

A typical agreement covers the help desk, security monitoring, backup, and support for the systems care runs on, from the electronic health record to every department's tools. Most providers add onboarding, offboarding, vendor management, and after-hours coverage, and security carries extra weight here because the data involved is protected health information.

Those line items describe labor, and labor is the smaller half of the value. A hospital generates a constant flow of access requests, application issues, and system changes, each carrying real PHI and downtime risk. When that flow lives in email and phone calls, response times can't be proven, and one change becomes a week of archaeology to explain. The intake and evidence layer is where managed IT succeeds or fails.

Regulated by HIPAA, not a rate card

Outsource, in-house, or hybrid: the decision under HIPAA

The model changes who's on the desk. It doesn't change what an auditor asks for.

Decision factorIn-houseOutsourced (managed services)Hybrid
Control over processFull control, shaped to the organizationProvider's playbook, tuned by contractOrganization sets process, provider works inside it
Evidence for audits and reviewsAs good as the organization's own tracking systemIn the provider's format, on the provider's systemOne shared system of record when the organization owns the platform
PHI exposureContained to organization staffExtends to provider staff under agreements and access controlsExtended only where access controls allow
Cost shapeFixed salaries, spiky project costsPredictable monthly fee, change orders for scopeBase team plus a scoped contract
After-hours & specialist depthThin unless the team is largeContractual coverage, 24/7 availableProvider covers nights and specialties, staff covers clinical judgment

Vivantio doesn't pick a model for you. It's the platform underneath whichever one you run, so the evidence trail looks the same no matter who's staffing the desk.

ITSM for healthcare on one platform

Every request captured. Properly. Not lost in a shared inbox.

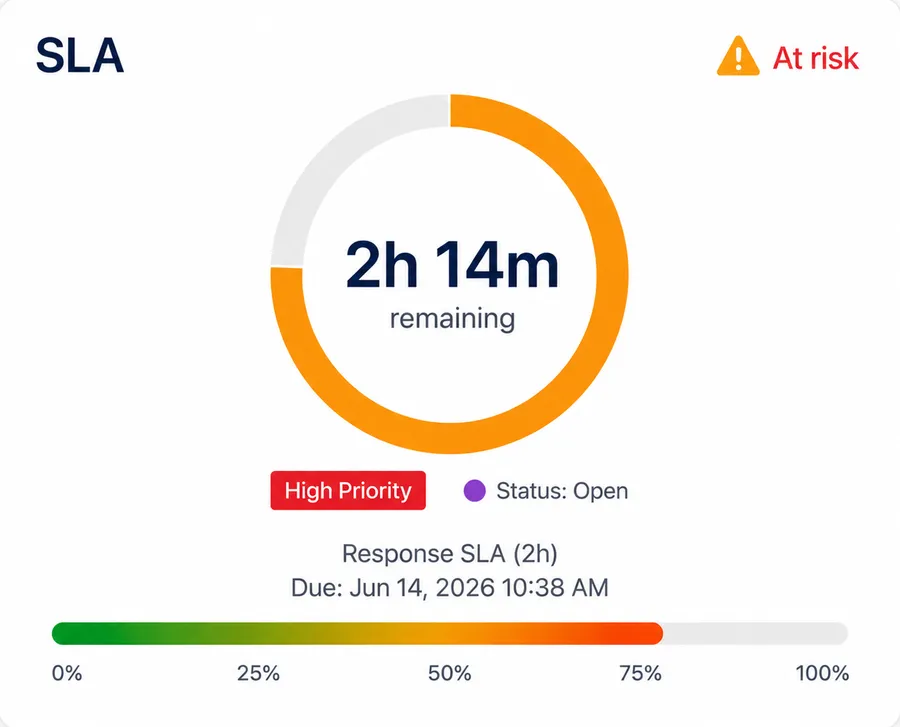
Vivantio gives healthcare organizations structured intake for every request type: access requests, clinical application support, equipment and facilities issues, and staff onboarding, so nothing arrives as an ambiguous email and nothing sits unowned. Response and resolution targets are tracked automatically, with escalation before an SLA breaches, not after.

  • Configurable intake forms per request type
  • SLA tracking with escalation before breach
  • Named ownership per request, no shared accountability
Explore SLA management
SLA tracking in Vivantio
HIPAA compliant service management, evidenced

Every action logged. Every viewer restricted. Every report exportable.

Vivantio's immutable activity log records every action on every request, change, and asset: timestamp, user, change, with role-based access control governing who can see and act on what. Vivantio is HIPAA compliant and holds ISO 27001, SOC 2, and Cyber Essentials Plus. Those are certifications of the platform; what HIPAA requires of your own organization stays your compliance team's call.

  • Immutable, timestamped activity log per request
  • Role-based access control (RBAC) across teams and data
  • Exportable audit reports for internal or external review
Explore audit & reporting
Platform certifications

Certifications you can verify

Vivantio holds ISO 27001 and SOC 2, is HIPAA compliant, and carries Cyber Essentials Plus. Those are certifications of the platform. What HIPAA requires of your organization stays your compliance team's call.

ISO 27001, SOC 2, HIPAA, Cyber Essentials Plus certifications

View certifications at trust.vivantio.com

Regulated change control

Every change approved first. Every change on record after.

Changes to systems that touch patient care need both. Vivantio's ITIL-aligned change management provides staged approval chains, a change calendar, and a full history on every change, so scheduled maintenance and emergency fixes alike leave the trail a reviewer expects to find. Every change links to the configuration items it touches, so the question of what changed and who approved it has a search, not a reconstruction.

  • Staged approval chains before changes go live
  • Change calendar across scheduled and emergency work
  • Full change history linked to configuration items
Explore change management
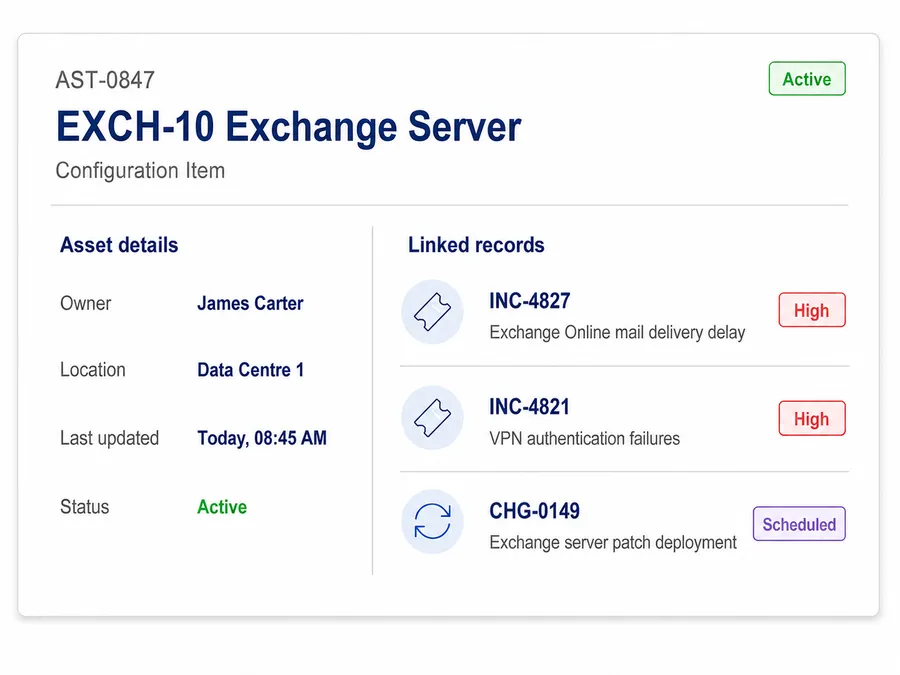
Configuration item record in Vivantio, linked to related incidents and changes
Asset management & CMDB

A record of record, not a spreadsheet someone forgot to update.

A healthcare estate spans workstations on wheels, department devices, servers, and the clinical applications that connect them. Vivantio's CMDB tracks all of it with relationships mapped, and it's included on every plan, not gated behind a higher tier, a real differentiator in a category where CMDB access is routinely a premium-edition feature elsewhere.

  • Full CMDB included on every plan, not a paid add-on
  • Assets linked to every incident, change, and request that touches them
  • Ownership and location tracked per asset, always current
Explore asset management
Asset and configuration item record in Vivantio
Complete service management platform

Everything else a healthcare organization's IT operation needs.

Self-service, automation, reporting and knowledge management, all included in your Vivantio licence, ready whether IT is run in-house, by a provider, or both.

Employee self-service portal

Clinical and administrative staff submit and track requests through a structured portal — no ambiguous email to the wrong inbox.

Automation & routing

Route each request type to the right team automatically — no manual triage, no shared inbox ambiguity.

Reporting & dashboards

Request volumes, SLA performance and audit exports, visible to leadership without a manual pull.

Policy & procedure knowledge base

Common staff questions answered at the portal, reducing routine enquiries to IT.

AI Assist

Included on every plan. Surfaces knowledge base answers in the self-service portal as staff type.

Beyond IT, on the same platform

Extend service management to facilities and clinical support functions, each in its own workspace.

Integrations

Connect to your identity and IT stack.

Vivantio connects to directory services, communication and reporting tools, no code required. Microsoft Teams, Azure Active Directory, Okta and hundreds more.

Microsoft TeamsAzure Active DirectoryOktaSlackMicrosoft ExchangeMicrosoft Power BIJiraSalesforce
Healthcare organizations on Vivantio

HIPAA-ready service management. Without the enterprise overhead.

0
%
Audit trail coverage
Every action logged. Every access recorded. Nothing happens in Vivantio without a timestamp and a user record.
0
wks
To go live
A dedicated consultant configures Vivantio around your request types, approval flows, and team structure. Fast.
0
★
Average G2 rating
Rated by IT, compliance and operations professionals — including teams like Enhabit.
Recognised across service management categories
G2 Leader — United Kingdom Service DeskG2 Leader — Enterprise Service DeskG2 Leader — Mid-Market Complaint ManagementG2 Leader — HR Service DeliveryG2 Leader — Mid-Market IT Asset ManagementG2 Leader — Mid-Market ITSMG2 Leader — IT Service Management
Healthcare organizations running on Vivantio

From spreadsheets to structured, auditable service management.

Vivantio has been trusted by clinical services organizations and complex, compliance-sensitive institutions to bring order to service requests that used to live in spreadsheets and shared inboxes.

SCP Health

One of the largest and fastest-growing healthcare organizations in the U.S., serving 8M patients a year across 400+ facilities, follows ITIL standards and streamlines reporting across service teams on Vivantio.

★★★★★We've reduced a 27-minute process to one click, and I couldn't be more excited.Michelle Tedder, Manager of Service and Support, SCP Health
Read the case study

Wake Forest University

A complex, compliance-sensitive institution with 25,000+ tracked assets runs access control and asset management on the same Vivantio CMDB healthcare organizations rely on for auditable service management.

★★★★★Vivantio's team helped us create a report that would total up the cost of the assets on a room-by-room basis and by university building. That report is going to help us immensely if we ever need to change rooms out or upgrade a facility.David Cowan, Physical Security Technology Administrator, Wake Forest University
Read the case study

Configured with you, supported as you grow

Our professional services team sets up your audit trail and compliance reporting during onboarding, then stays on to help you extend it as your needs evolve.

★★★★★I've worked in IT for 35 years, and I cannot think of another vendor that gets support so right, so often.G2 Review · IT Professional

Serving healthcare clients as a provider?

IT providers serving hospitals, health systems and practices run client-facing delivery on Vivantio with multi-team structure, per-client SLAs and reporting built for quarterly reviews. Vivantio covers the service management layer; providers pair it with their own security and infrastructure tooling.

See Technology and Service Providers
Common questions

Managed IT for healthcare: what teams ask us

What are managed IT services for healthcare?

They are outsourced IT operations for hospitals, health systems, and practices, typically covering the help desk, security monitoring, backup, and support for clinical and administrative systems under a monthly agreement. Many organizations run hybrid models, keeping clinical-system oversight in-house while a provider supplies depth and after-hours coverage.

Should a hospital or health system outsource IT support?

Smaller organizations often gain coverage and specialist depth by outsourcing, while larger ones tend to run hybrid models. Either way, the organization should own its service management platform, so request history, access records, and audit evidence stay continuous across any provider relationship.

Is Vivantio HIPAA compliant?

Yes. Vivantio is HIPAA compliant and holds ISO 27001, SOC 2, and Cyber Essentials Plus, with details published at trust.vivantio.com. Those are certifications of the platform, and they equip your organization to answer its own diligence and compliance questionnaires with specifics.

Is Vivantio suitable for healthcare and regulated organizations?

Yes. Vivantio is HIPAA compliant and holds ISO 27001 and SOC 2, with audit trails and role-based access suited to regulated environments. Wake Forest uses Vivantio for service management across a complex, compliance-sensitive organization.

Does Vivantio provide immutable audit trails for compliance?

Vivantio records a full history of actions on tickets, changes, and assets, giving compliance and security teams a defensible record of who did what and when. Combined with role-based access, that supports evidence requirements across standards.

Can Vivantio scale service desk operations across a large healthcare organization?

Yes. Vivantio runs service management for IT and for other departments on one platform, so a hospital or health system can support clinical, facilities, and administrative teams under a single, auditable system that scales with the organization.

Does Vivantio integrate with security and GRC tooling?

Vivantio connects to your wider stack through its integration layer and API. Teams needing specific SIEM or GRC connectors should confirm the integration path with Vivantio during scoping, as depth varies by tool.

Healthcare organizations on Vivantio

Ready to make evidence a byproduct of the work

We'll show you how Vivantio handles structured intake, SLA tracking, asset management and the audit trail a HIPAA review actually asks for, configured around your organization. Most teams go live in three to four weeks through Vivantio's Rapid Deployment System, and every capability on this page ships on every plan, so the renewal price is the price you modeled on day one.

~30-minute demo No ITIL jargon required Full audit trail from day one